
// 19 March 2027 · Sibiu
Masterclass Day
Executive-level, practitioner-led sessions that turn cyber risk into decisions. Go beyond the main stage: learn where to start, what to prioritise and how to build real cyber resilience in your organisation.
4 masterclasses · 2 parallel slots
Pre-registration required · Certificate awarded
// Why a masterclass
From awareness
to action.
Every organisation depends on its IT systems and the integrity of its data — yet protecting them can feel like a never-ending effort. Our masterclasses give leaders a clear, risk-based starting point and the practical tools to move from conventional security measures to lasting cyber resilience.
01 //
Risk-based thinking
Identify, assess and prioritise the cyber risks that matter most to your business, and align security with strategy.
02 //
Real-world cases
Lessons from actual incidents, live demonstrations of common attack methods and the questions to ask before they happen to you.
03 //
Interactive format
Short lectures, practical exercises, group discussions and scenario work — with experts on hand to answer your questions.
04 //
Certificate
Small groups, focused content and a certificate of participation for every attendee who completes the session.
// 2027 masterclasses
Four sessions.
Two parallel slots.
Held on Friday, 19 March 2027, alongside Congress Day 2. Pick one session per slot when you register — seats are limited.
NIS2 for Balkan Institutions and Businesses
What the directive requires in practice, who is in scope, and how to build a realistic roadmap for governance, risk management and incident reporting.
Trainer · to be announced
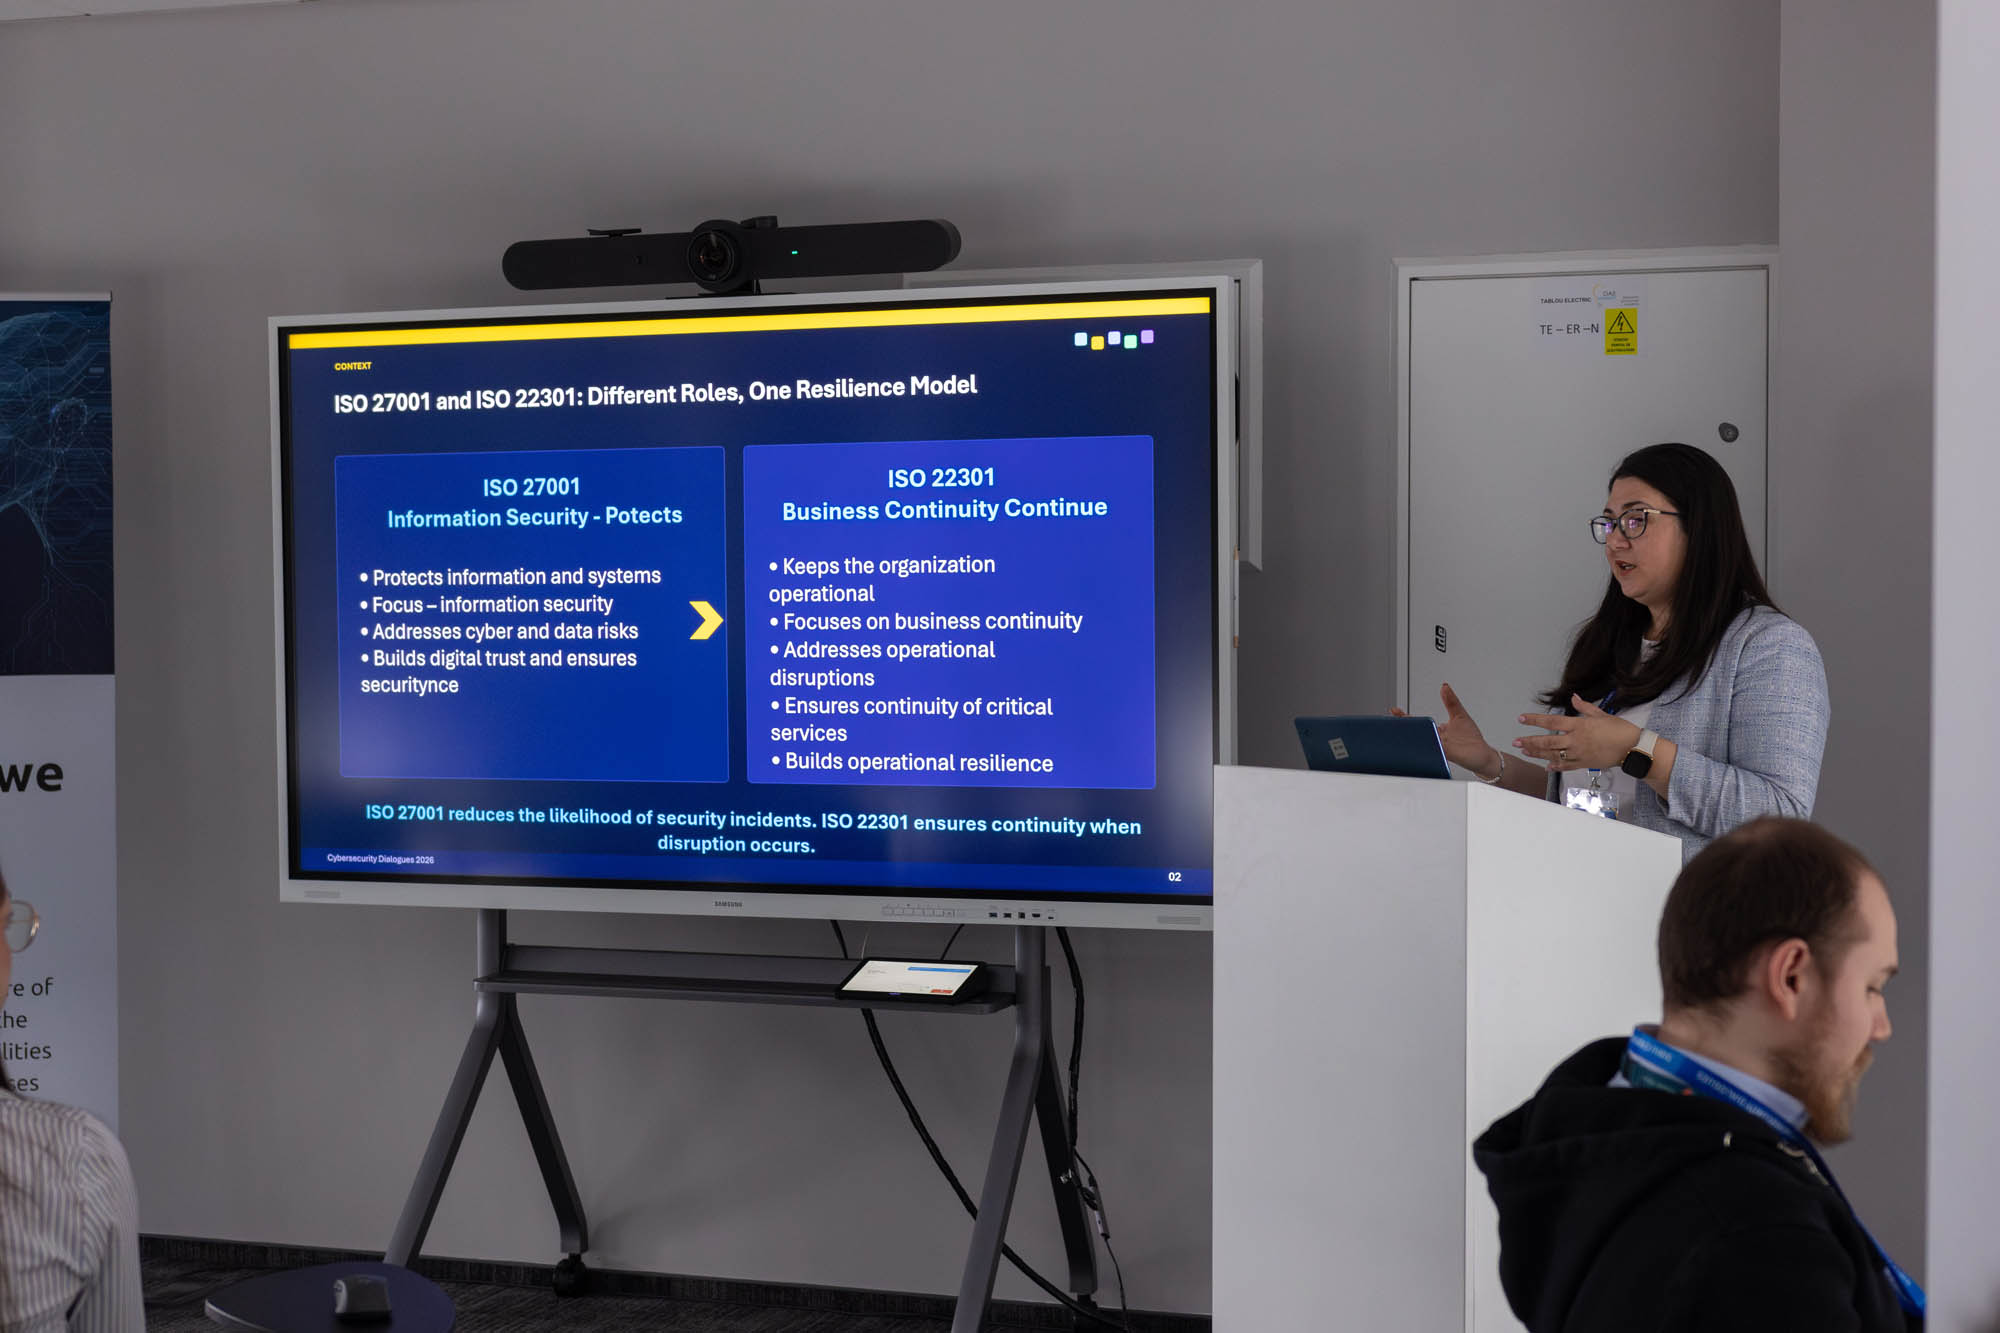
Resilience by Design: Applying ISO 22301 & 27001 to Public-Private Ecosystems
Use business impact analysis and recognised frameworks to design continuity and incident response that hold up when a real crisis hits.
Trainer · to be announced
Inclusive by Design: Gender, Diversity, and the Architecture of Human Security
People are the first line of defence. Build a security culture and awareness programme that reaches everyone in the organisation.
Trainer · to be announced
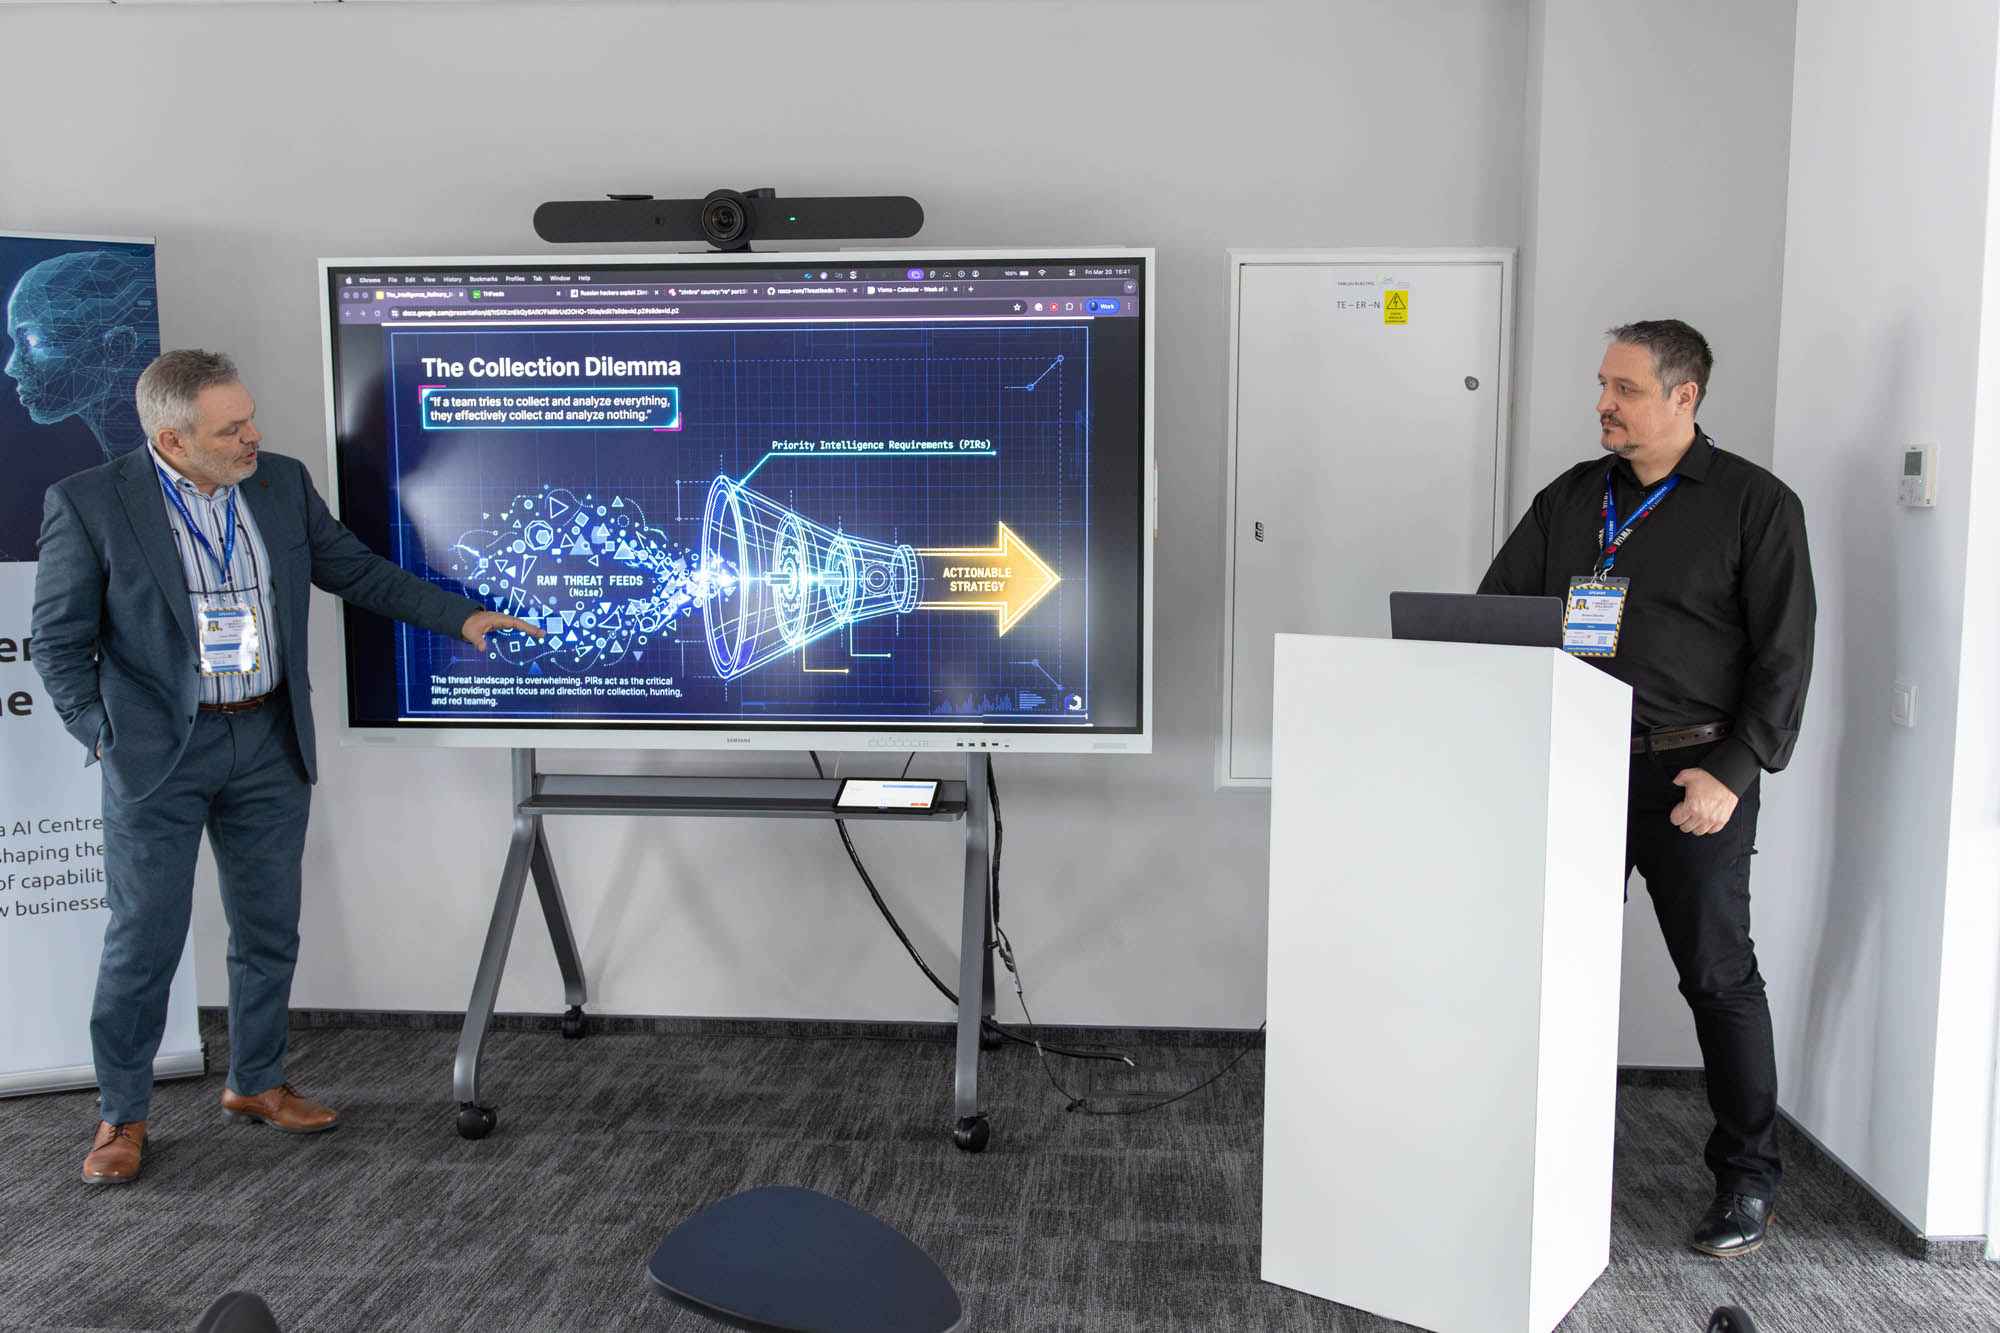
Cyber Threat Intelligence: From Data to Actionable Strategy
Map the current threat landscape, understand common attack methods and turn intelligence into decisions your executive team can act on.
Trainer · to be announced
// What you take away
Key learning objectives
→ Understand cyber resilience and how it differs from traditional security practice.
→ Locate, assess and prioritise the cyber risks specific to your organisation.
→ Run a business impact analysis to see what an incident really costs — in operations, finances and reputation.
→ Tailor recognised frameworks such as NIST CSF and ISO 27001 to your own needs.
→ Build an incident response plan that minimises downtime and damage.
→ Create a security culture and a feedback loop for continuous improvement.
// Who should attend
Built for decision-makers
→ Executives and members of management teams
→ CISOs, IT and security managers
→ Risk, compliance and business continuity professionals
→ Leaders of public institutions responsible for cybersecurity decisions




// 18–19 March 2027 · Sibiu
Seats are limited. Reserve your masterclass.